On 11 November 2026, PANews reported that Ethereum Layer 2 Scroll had posted a notice on its governance forum about a vulnerability in the bundle proof verification contract on Ethereum mainnet. PANews described the response as a completed emergency mainnet upgrade.
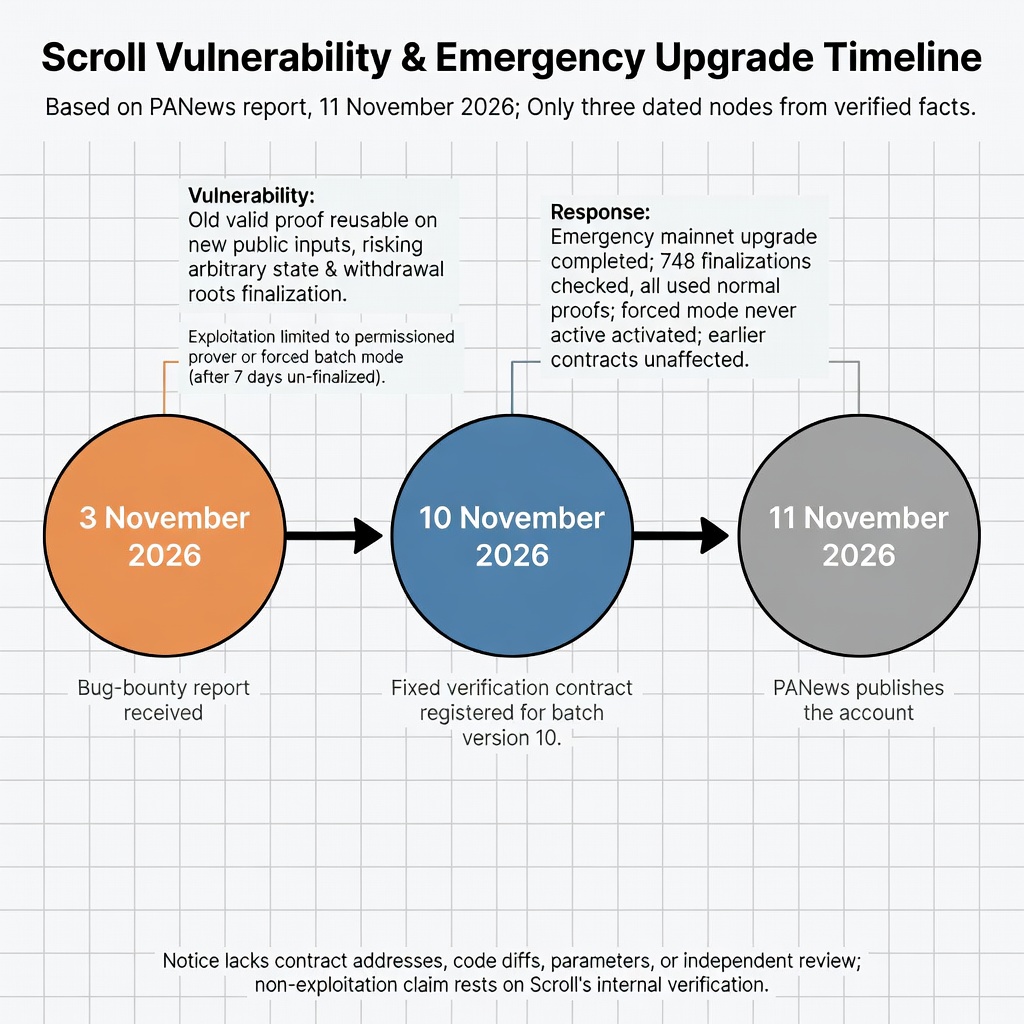
Scroll said it received the bug-bounty report on 3 November 2026. On 10 November 2026 it registered a corrected verification contract for batch version 10.
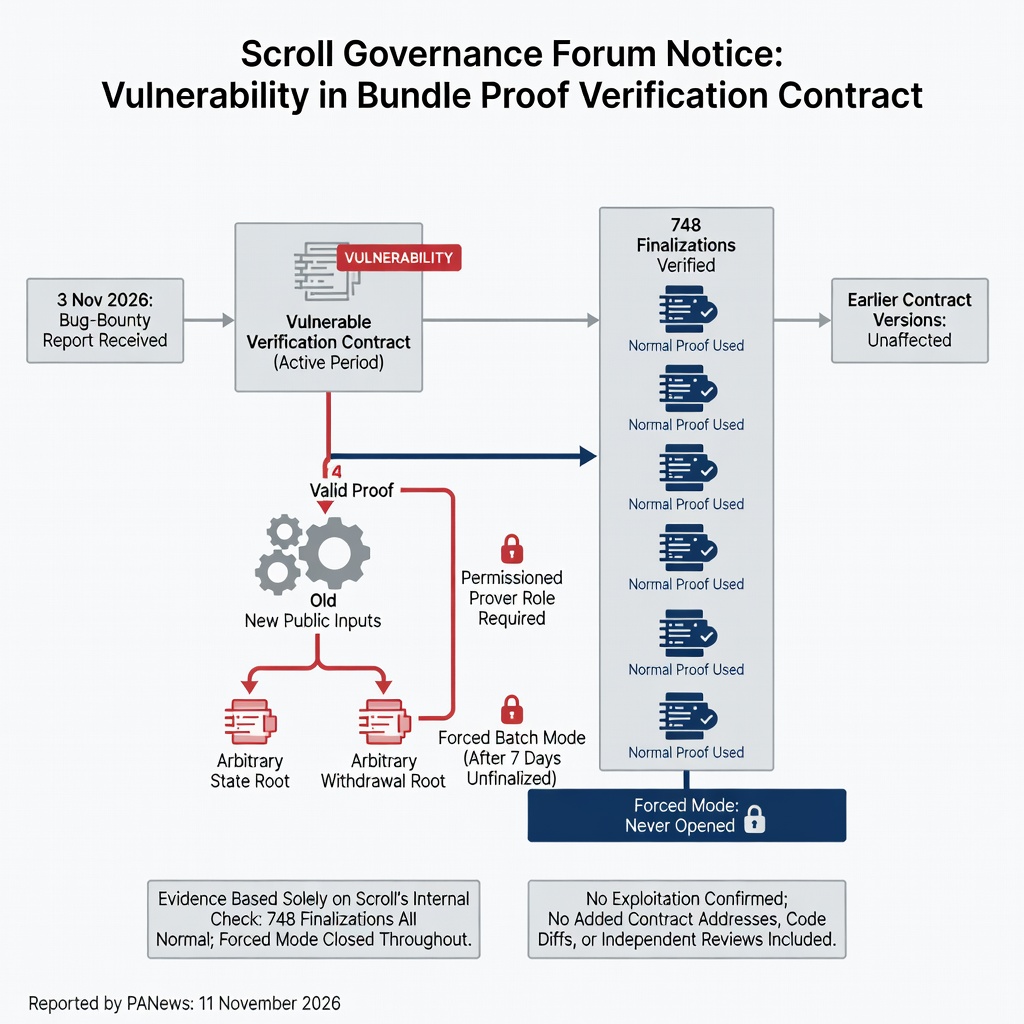
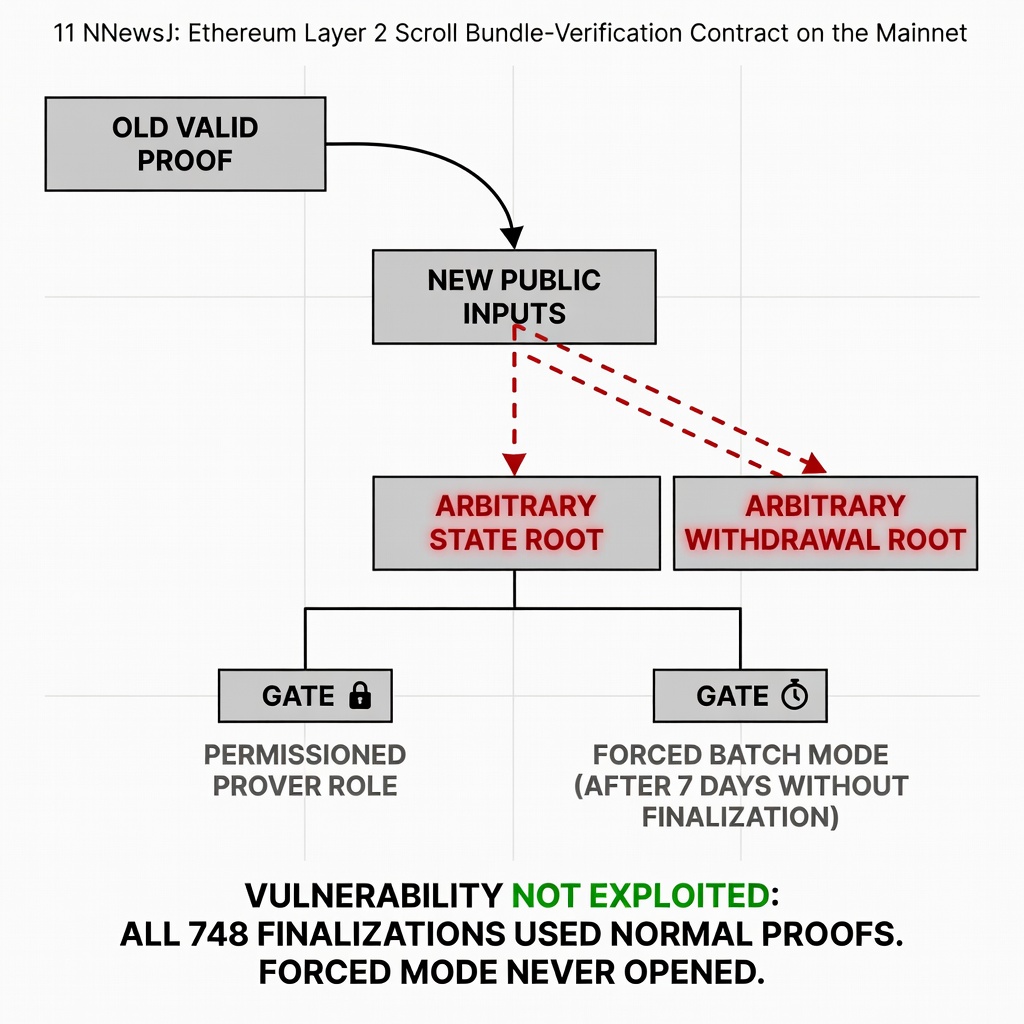
As described in the notice, the flaw let an old valid proof be applied to new public inputs. That reuse could have been used to finalize arbitrary state roots and withdrawal roots. Exploitation was not open to an arbitrary caller. It required the permissioned prover role, or the forced batch mode that opens only after seven days without finalization.
Scroll stated that it had checked the period in which the vulnerable verification contract was active and that the flaw was not exploited on mainnet. All 748 finalizations in that period used normal proofs. Forced mode was never opened. Earlier versions of the verification contract were not affected.
The notice, as relayed by PANews, does not include contract addresses, a code diff, proof-system parameters, or an independent review. The claim that the bug was not exploited rests on Scroll’s account of those 748 finalizations and on its statement that forced mode stayed closed.
Original article: PANews, 11 November 2026